
Identity Security Without Compromising Convenience
Okta IAM Solutions | Master Concept
Okta is a cloud-native IAM platform that unifies access for employees, customers, and AI agents — making identity governance more visible, controlled, and auditable.
Learn More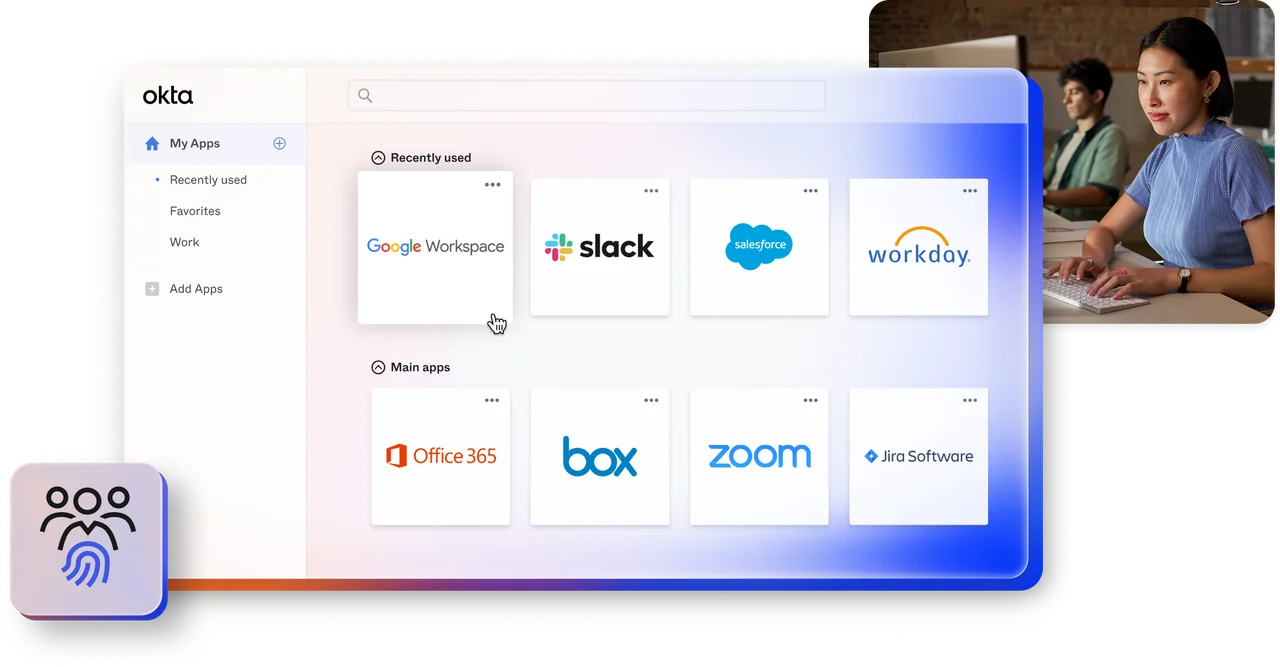
Why Identity Security
Matters Now
Cloud, hybrid work and AI have moved access beyond the traditional network perimeter. The question is no longer only who is on the network, but which identity — human or non-human — can reach which resource.
Most enterprise access now falls into three groups:
 Internal workforce: employees and contractors issued formal enterprise accounts
- External users: customers and partners who need access without becoming internal users
- Non-human identities: AI agents, service accounts, bots and automated workflows


Their risks differ, but all three require clear policy, lifecycle control and auditability.
 SECTION 01
Scenario A | Internal workforce: fragmented identities create access debt
"We’re running AD, Microsoft Entra ID and Google Workspace side by side. Staff juggle several passwords, and a few legacy systems can’t be connected to SSO at all, so IT manages those separately."

 Common scenarios
- •New hires wait a week for accounts while accounts remain active three months after an employee leaves.
- •An audit asks who can reach which systems, and IT spends days assembling the list
- •A few systems only work with shared logins, and nobody is sure who is using them now
SECTION 01For A | Employees and contractors
SSO + Adaptive MFA: provide one sign-in experience while increasing verification only when risk or application sensitivity requires it.
Universal Directory + Lifecycle Management: unify sources such as AD, Microsoft Entra ID and Google Workspace, then automate joiner, mover and leaver access.
Access Gateway: bring legacy on-premises applications under the same access policy without rewriting the application.
Identity Governance: add access requests, reviews and entitlement visibility to support audits.
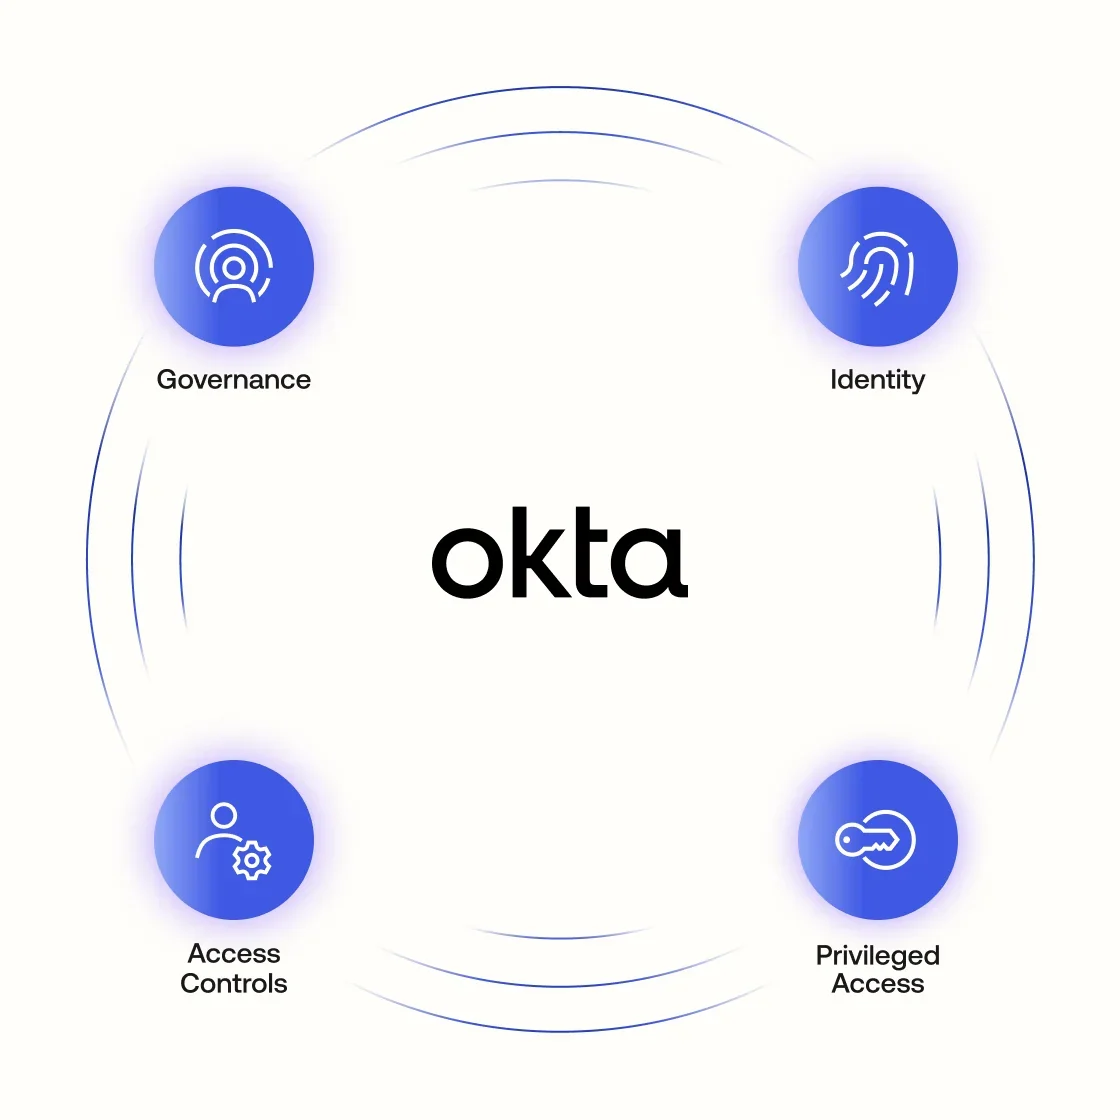
Privileged Access: enforce least privilege for administrators and critical resources.

Proof point: a Forrester Consulting Total Economic Impact™ study commissioned by Okta reported 211% ROI and payback in under six months for a composite organisation. Results are modelled and do not represent a single customer.
SECTION 02Scenario B | External users: secure access without treating customers and partners as employees
"Customers should be able to sign up quickly and log in securely. Channel partners need to check orders and pull reports. But building and maintaining our own authentication system is too costly, and giving partners internal accounts isn’t safe."
Common scenarios- •Customer password reset tickets are frequent enough to need dedicated support time
- •Partners need reports, and today that means emailing files or opening a VPN for them
- •The product should support newer login methods such as social login and passkeys, but they cannot be prioritised in the development schedule.
SECTION 02For B | Customers and partners
- For customer identity, Okta offers two approaches:
Auth0: developer-first, for teams that want to build and customise sign-up, login and authorisation in their own products.
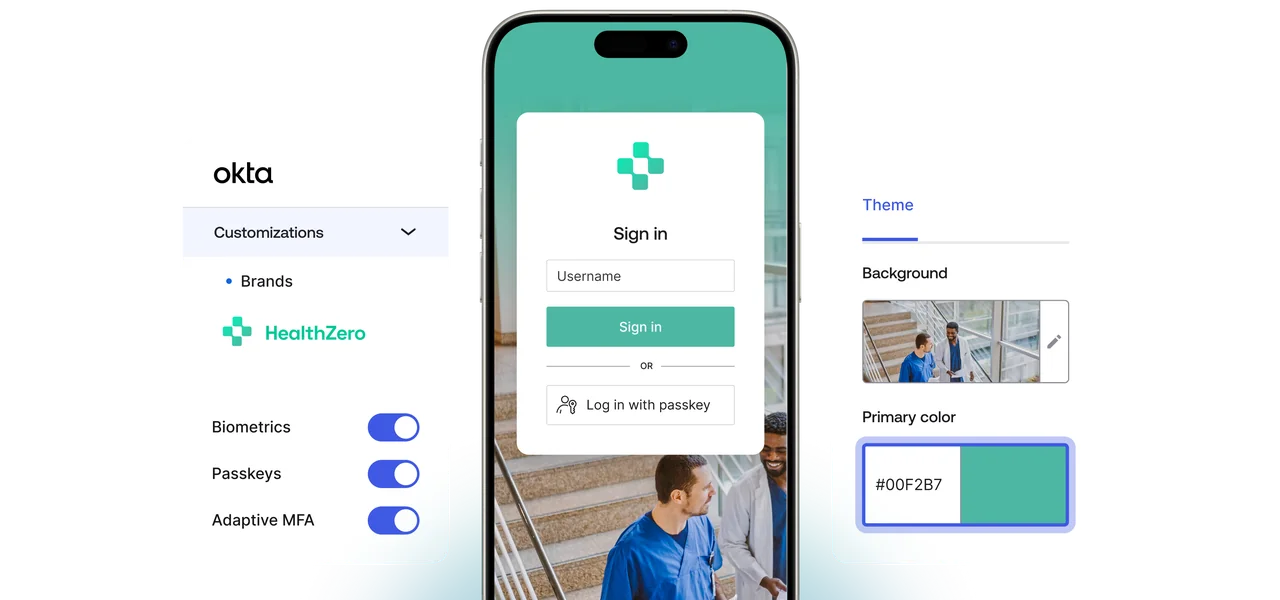
Okta Customer Identity (OCI): built on the Okta platform for enterprise teams that prefer scalable, low-code or no-code customer login policies, including multi-brand use cases.
- For partner and external access:
Secure Partner Access: gives partners controlled access without treating them as internal employees.
API Access Management: protects APIs exposed to external applications and partners with centralised authorisation policies.
The result is a cleaner separation between workforce identity and external access, without creating a second set of unmanaged credentials.
SECTION 03Scenario C | Non-human identities: AI agents and service accounts with no clear owner
"Employees have started using various AI tools, but we can’t see who is using them or what data AI agents are accessing. Same with the service accounts between systems – those passwords have never been rotated."
Common scenarios- •Colleagues are already using AI tools to process customer or internal data, and no one has the full list
- •Passwords for system-to-system integration accounts are stored in configuration files and have never been rotated.
- •An automated workflow can access the production database, and it runs under the account of a former employee.
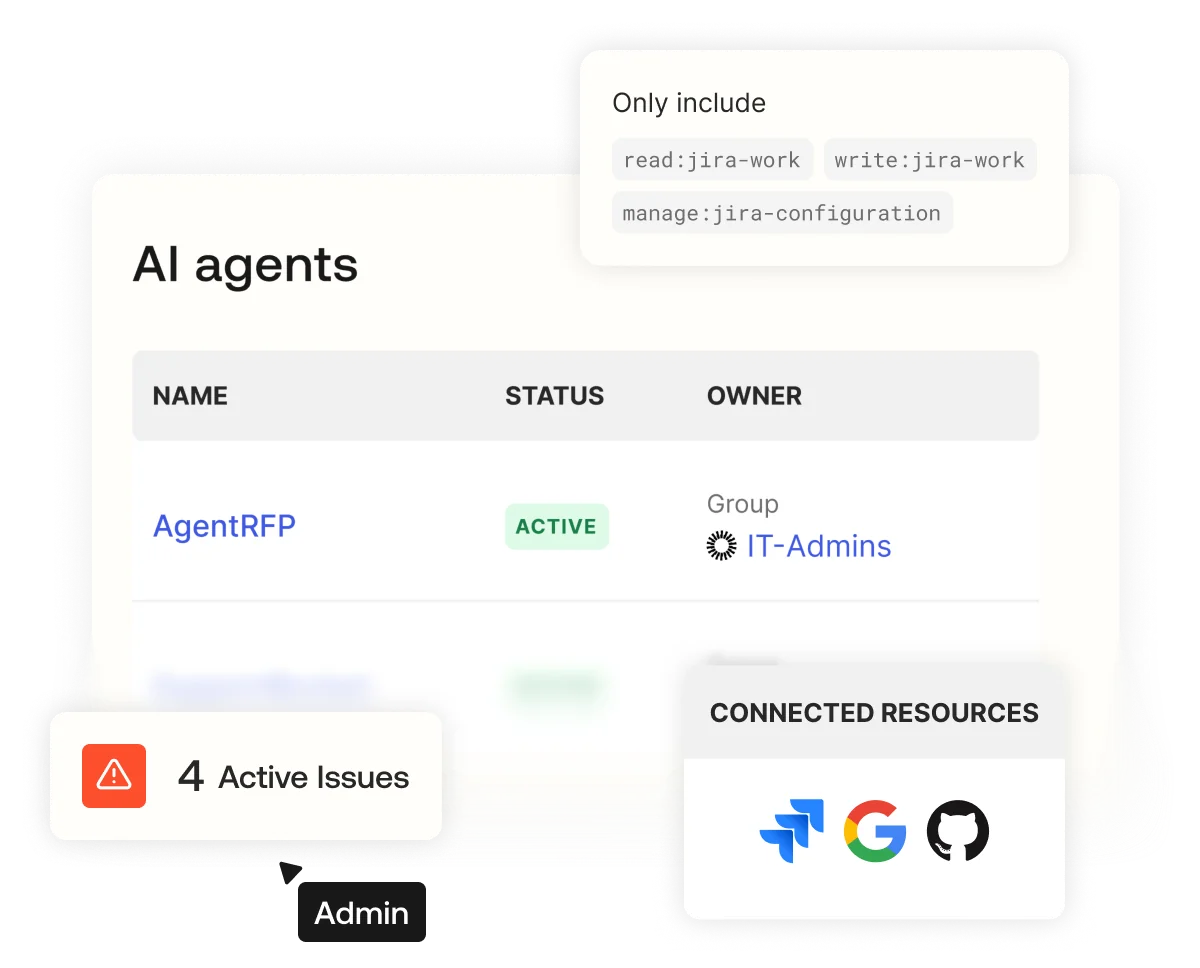
 What are non-human identities (NHI)?SECTION 03
For C | AI agents and service accounts
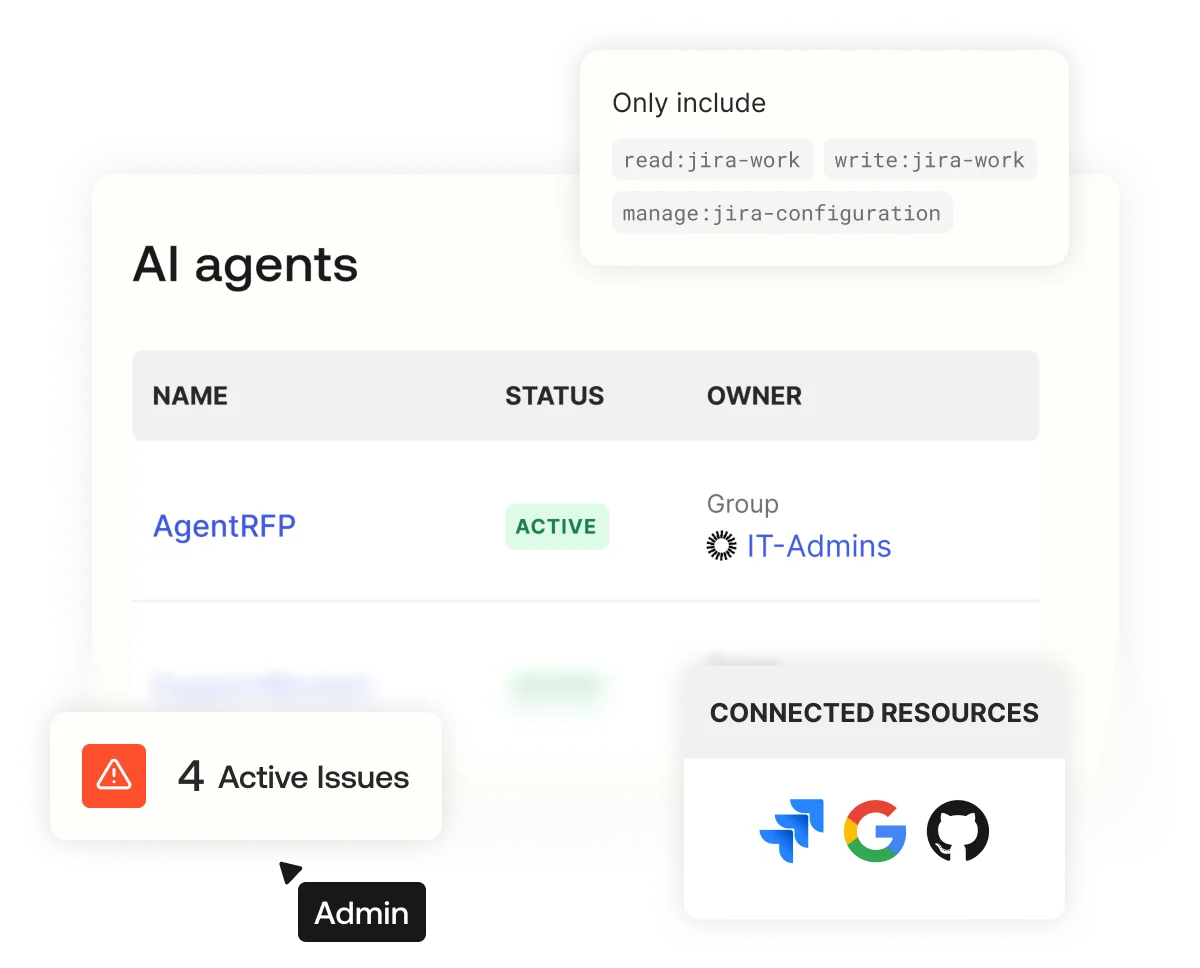
Okta for AI Agents: gives AI agents identifiable identities, ownership, policy-based access and auditable activity.
Cross App Access Protocol: supports controlled cross-application access without relying on shared keys or broadly privileged accounts.
Auth0 for AI Agents: adds identity and authorisation controls to AI applications built by development teams.
Privileged Access: applies least privilege to service accounts, shared accounts, break-glass accounts and bots, with stronger visibility over sensitive access.
This gives security teams a clearer answer to four questions: which agents exist, who owns them, what they can access and how that access can be revoked.
Okta Capabilities
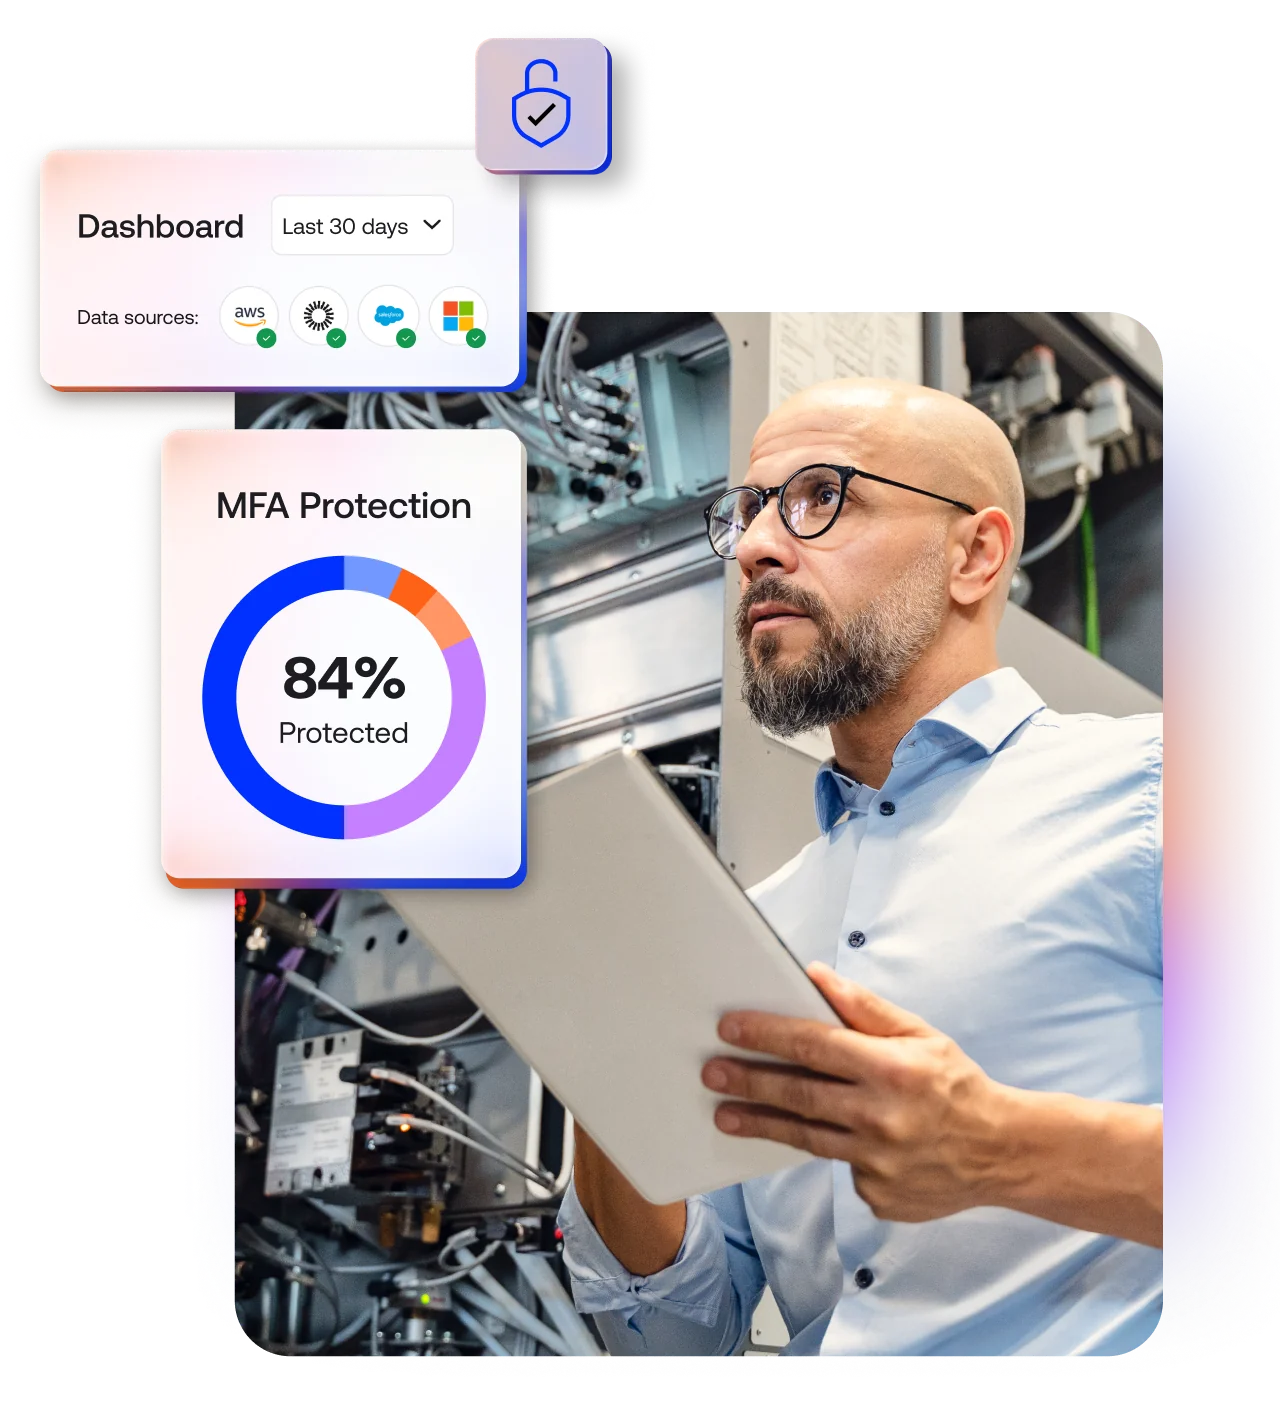
SSO, Adaptive MFA and FastPass simplify access while increasing authentication strength when risk rises.
Single Sign-On (SSO): connects applications through standards including SAML 2.0, OIDC and WS-Federation; SWA can support applications without federated login.
Adaptive MFA: evaluates signals such as device, network, location, IP and user behaviour, stepping verification up for higher-risk access and working with ThreatInsight.
FastPass: passwordless, phishing-resistant authentication using Okta Verify.
Access Gateway, Secure Partner Access and API Access Management extend consistent access control across legacy apps, partners and APIs.
Access Gateway: protects on-premises web applications using methods such as Kerberos, IWA and header-based authentication without changing application code; supports common enterprise applications including Oracle EBS, PeopleSoft, JD Edwards and SharePoint.
Secure Partner Access: separates partner populations and can delegate user, group and application administration to partner administrators.
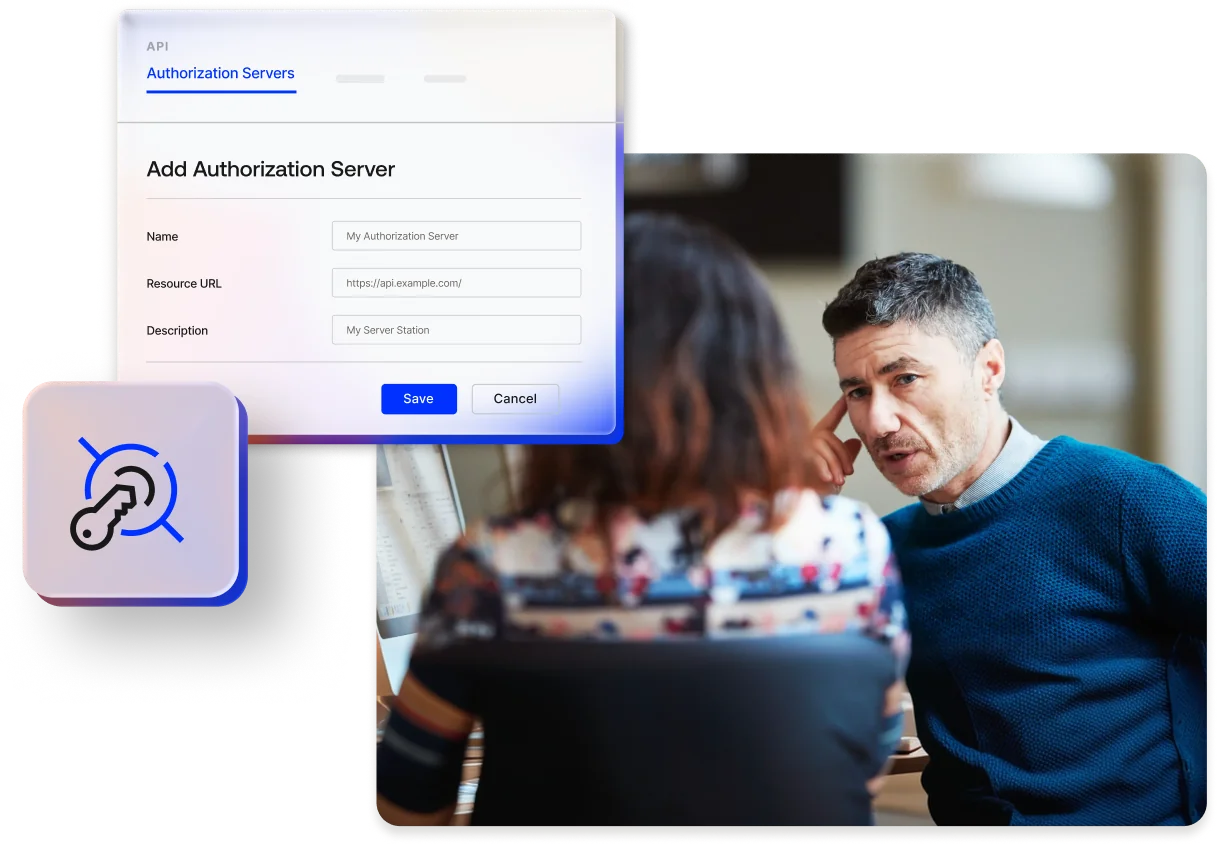
API Access Management: uses custom OAuth 2.0 authorisation servers, scopes, claims and access policies to protect enterprise APIs.
Universal Directory, Lifecycle Management and Identity Governance centralise identity data and automate access across the user lifecycle.
Universal Directory: connects identity sources such as AD/LDAP, HR systems and SaaS applications through profile mapping and centralises users, groups and devices.
Lifecycle Management: automates provisioning and deprovisioning using SCIM, Okta Integration Network connectors and on-premises provisioning.
Identity Governance: supports access requests, approvals, certification campaigns, entitlement management and audit reporting.
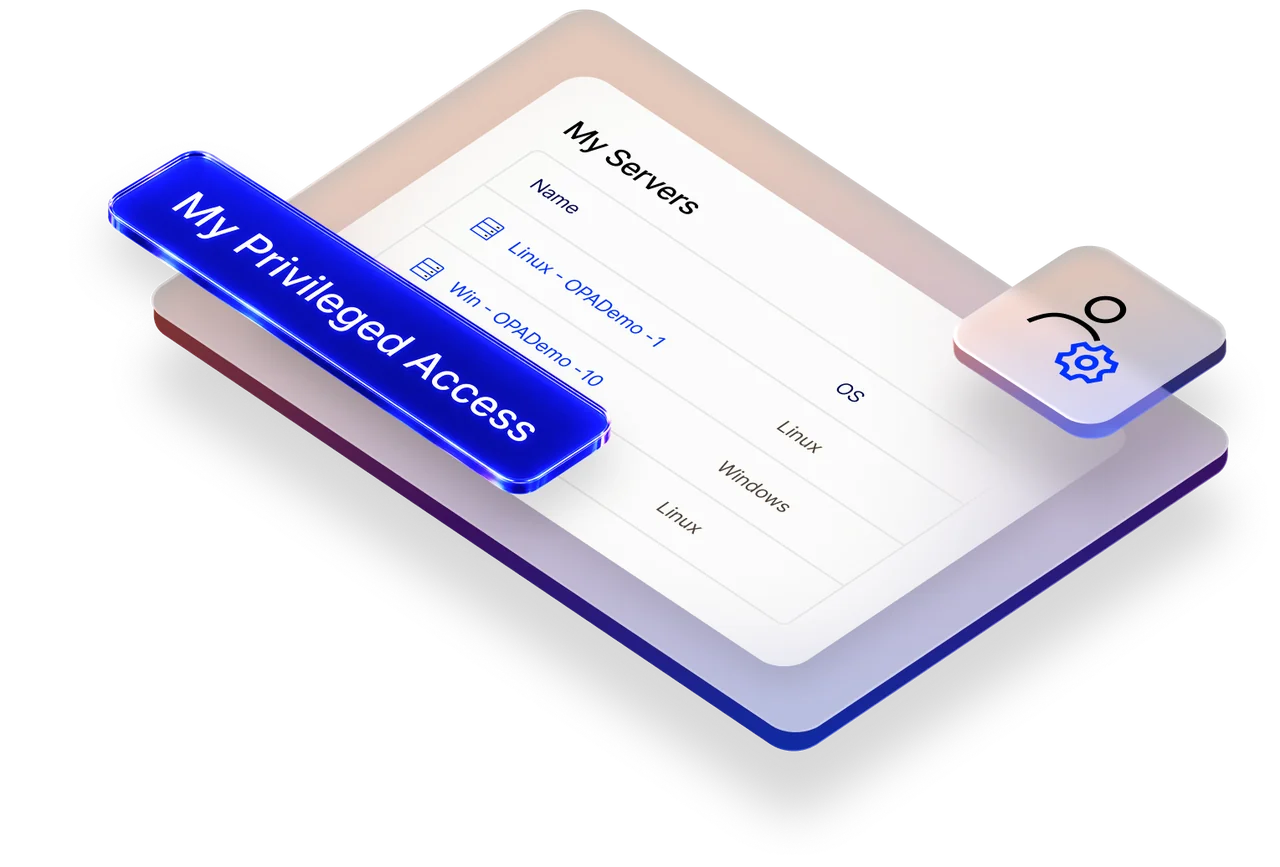
Privileged Access and Advanced Server Access apply least privilege to administrators, servers, databases and high-risk credentials.
Privileged Access: supports just-in-time elevation and short-lived credentials across SSH/RDP, Kubernetes and databases, with credential vaulting, rotation and session visibility.
Advanced Server Access: issues short-lived OpenSSH or X.509 client certificates, replacing static keys and passwords while supporting sudo-level control and server audit logs.
ISPM and Identity Threat Protection with Okta AI surface identity risk and respond to suspicious activity before and after login.
Identity Security Posture Management (ISPM): identifies identity weaknesses and misconfigurations across cloud and SaaS environments and prioritises them by risk.
Identity Threat Protection with Okta AI (ITP): continuously evaluates session risk after login, combines signals such as behaviour, network and device state, and can trigger re-authentication or sign-out through shared security signals.
Auth0 and Okta Customer Identity support secure, scalable login experiences for customers and external users.
Auth0: a separate developer-focused platform and admin experience for building sign-up, login and authorisation with SDKs and APIs.
Okta Customer Identity (OCI): runs on the Okta platform and provides low-code/no-code policy configuration for external users, including multi-brand scenarios.
Okta for AI Agents, Cross App Access Protocol and Auth0 for AI Agents bring ownership, authorisation and auditability to AI-driven access.
Okta for AI Agents: discovers and governs AI agents, assigns human ownership, protects credentials, controls API access and supports access reviews.
Cross App Access Protocol: extends OAuth/OIDC concepts to support short-lived, scoped cross-application access while keeping the authorisation decision with the identity provider.
Auth0 for AI Agents: adds capabilities such as secure token handling, fine-grained authorisation and human approval for AI workflows.
From Assessment to
Continuous Governance
Okta works best as part of an identity architecture, not as a standalone login tool. Master Concept structures the rollout around four stages so security, integration and operational resilience progress together.
Assess
Inventory identity sources, applications and access paths; identify risk, compliance requirements and priority use cases. The outcome is a phased scope aligned to business impact.
Integrate
Start with high-value controls such as SSO and MFA, then connect directories, lifecycle processes and existing SaaS or on-premises applications. Integration is phased to reduce disruption rather than force a big-bang migration.
Govern
Automate joiner, mover and leaver access, introduce access reviews and privileged controls, and extend governance to partners, service accounts and AI agents where required.
Optimise
Use dashboards and periodic reviews to refine entitlements and risk policies. Resilience is designed in from the start through break-glass accounts, fallback access for critical applications and documented incident procedures; a vendor SLA should not be the only safeguard.
Common Challenges and
Solutions Across Industries
Government, Public Sector and Education
Common challenge: Hong Kong government departments, public bodies and higher education institutions often support large populations of civil servants, employees, faculty members, students, alumni and external users, while maintaining applications and identity systems built across different generations of technology.
How Okta helps: Universal Directory and SSO integrate fragmented account systems. At City University of Hong Kong, Master Concept helped unify authentication across 90% of its applications and digital services, improving access visibility and user experience for staff, students and alumni.
Further reading: City University of Hong Kong | Federal Government
Financial services
Common challenge: Hong Kong’s BFSI (Banking, Financial Services and Insurance) organisations operate across a complex mix of on-premises, cloud and SaaS environments. As they modernize their technology infrastructure, they must strengthen identity and access controls without compromising security or regulatory requirements.
How Okta helps: Zero Trust architecture enforces access control while providing a simple and secure user experience, reducing risk exposure during digital transformation. Modern Treasury uses Okta Identity Governance to establish a trusted foundation for employee access from day one.
Further reading: Nasdaq | Modern Treasury
Retail
Common challenge: Hong Kong’s retail, hospitality, F&B and tourism businesses often operate large frontline and mobile workforces across multiple locations. Frequent workforce changes and fragmented identity data across HR, POS, ERP and enterprise applications can make access management difficult and increase security risk.
How Okta helps: consolidating HR systems centralises employee records, and SSO and MFA replace manual approval, improving efficiency while strengthening access security for internal systems. Beauty retailer Sephora had been running three independent HR systems; after adopting a single HR system as its identity source, it deployed to 36,000 employees across 36 countries in six months and brought 102 applications under SSO and MFA. Because 88% of those applications had pre-built integrations, Sephora saved roughly 14 months of integration effort.
Further reading: Sephora
Why Master Concept
Master Concept is an Okta partner in Asia Pacific. In 2026 it received the Okta Catalyst Award for Strategic Excellence and was promoted to the next tier of the Okta partner program, in recognition of the performance of its identity security practice during the financial year and the continued strengthening of the partnership.
Master Concept is also an implementation partner for joint Okta and Google Cloud solutions, integrating identity, cloud and AI governance capabilities. It has helped leading universities across Asia to simplify authentication across applications while maintaining high security standards.
Questions
You May Have
Typical signals include a growing SaaS estate, on-premises applications that still need central control, or access that extends to contractors and partners. Okta provides a neutral identity layer with 8,000+ pre-built integrations to bring these environments under consistent policy.
Use Okta for workforce and enterprise access; use Auth0 when development teams need to build customer sign-up, login and authorisation into their own products. Organisations with both needs can use both.
No. Okta usually integrates with existing directories rather than replacing them. Sources such as AD, Microsoft Entra ID and Google Workspace can feed into a unified identity layer while Okta adds SSO, MFA, lifecycle and governance capabilities.
It depends on application volume and identity complexity. Okta reports that around 25% of new Identity Governance customers go live within 30 days and more than 50% within six months; Master Concept recommends a phased timeline after assessment.
Yes. The better measure is identity complexity, not employee count. Organisations using multiple SaaS applications or supporting remote and hybrid access can start with a focused scope and expand over time.
Resilience should be designed beyond the vendor SLA. Okta publishes 99.99% platform uptime, while Master Concept also plans break-glass administration, fallback paths for critical applications and documented incident procedures.
The same core principles apply: give the identity an owner, define what it can access and make access revocable and auditable. Okta for AI Agents and Privileged Access extend those controls to AI agents, service accounts, shared accounts and bots.

